Intent-driven network access & connectivity · v1.0.0 GA
Define the network you mean.
JANUS is an intent-driven network access and connectivity platform. Define who or what should reach which resources — JANUS resolves that intent into network state and tracks whether the intended state has actually been applied.
A tunnel is not access.
VPNs and network connectivity make resources reachable — but reachability is not authorization.
Traditional connectivity starts with a tunnel and then accumulates routes, firewall rules, NAT, user and group configuration, site-specific exceptions and operational dependencies. The tunnel itself never answers the question that actually matters: should this identity be allowed to use this resource at all?
JANUS starts from that question. It decides first, then builds and enforces the path.
Identity. Policy. Path. Enforcement.
JANUS creates a central control plane for secure, identity-aware access and enforces policy through distributed gateways.
- One control plane for identity, access rules, routing and enforcement.
- Policy decides before any path is built — the network path is never the authorization.
- Gateways stay distributed: in your sites, data centers, clouds and existing networks.
- Your routers, firewalls and addressing stay where they are. JANUS adds the control layer.
- Every decision is explainable, and desired state is kept separate from runtime truth.
POLICY FIRSTPATH SECONDDENY BY DEFAULTLEAST PRIVILEGE
Built for real infrastructure
- Intents & Services
- Sites, Resources & Groups
- Roadwarrior Enrollment
- Site Connections & Site Edges
- Activity · Reconciliation · Audit
- Multi-Gateway & Multi-Ingress
- Multi-Tenant Isolation
- Overlapping Networks
- MFA & Passkeys
- LDAP & Active Directory
- Runtime Observability
- Explain Access
- IPv4 & IPv6
An intent-driven network access and connectivity platform.
Humans describe intent. JANUS resolves representation — one logical operator Intent stays one logical object even when JANUS needs several runtime artifacts to realise it.
JANUS gives operators one model for defining access, network resources, sites, remote devices and connectivity, and resolves those intentions into runtime configuration while continuously reconciling desired and applied state.
WireGuard is one transport technology within the data plane. The actual product sits above it: JANUS determines and technically enforces who or what may access which resource, over which path, and under what conditions.
Know when intent becomes reality. APPLIED means fully applied — saving a configuration is not proof that the network changed.
Intent instead of tunnel building
Describe who may reach what. JANUS derives the path and the enforcement.
Git is the source of truth
Administration produces declarative desired state — versioned, reviewable, reproducible.
Distributed gateways
Gateways run where the networks are, coordinated from one control plane.
Keep existing infrastructure
Your routers, firewalls and addressing remain in place.
Policy first. Network path second.
Reachability ≠ Authorization
A reachable resource is not a permitted one.
NAT ≠ Authorization
Translation enables connectivity. It grants nothing.
Saved ≠ Applied
Saving a configuration is not proof that the network changed. JANUS treats missing evidence as not success.
Network Path ≠ Security Identity
Arriving on the right wire is not the same as being the right principal.
Deny by Default
Nothing is allowed because it happens to be present.
Least Privilege
Access is as narrow as the requirement, and explicit.
We do not derive trust from assumptions.
Distributed connectivity — isolated per deployment.
Inter-Gateway Fabric
Gateways reach each other under policy — the fabric is not implicitly trusted.
Multi-Ingress
A user may arrive through one gateway and reach a resource behind another.
Shared & Dedicated
Dedicated or shared infrastructure, with isolated runtime per deployment.
Overlapping Networks
Address spaces may overlap across deployments without collisions.
Identity belongs in the access decision.
JANUS separates identity, authentication, administrative authority and resource authorization.
LDAP / Active Directory
Authenticate administrators and end users against an existing LDAP directory or a Microsoft Active Directory forest, and map directory groups to JANUS roles.
Identity federation (OIDC)
Connect Microsoft Entra ID, Keycloak, Okta or any standards-conformant OpenID Connect provider.
MFA
Multi-factor authentication for administrative and user access.
Passkeys / WebAuthn
Hardware-backed credentials where the browser and platform support them.
Service / API Identities
Workloads authenticate as first-class principals, not shared secrets.
Scoped RBAC
Administrative authority is scoped, not global by default.
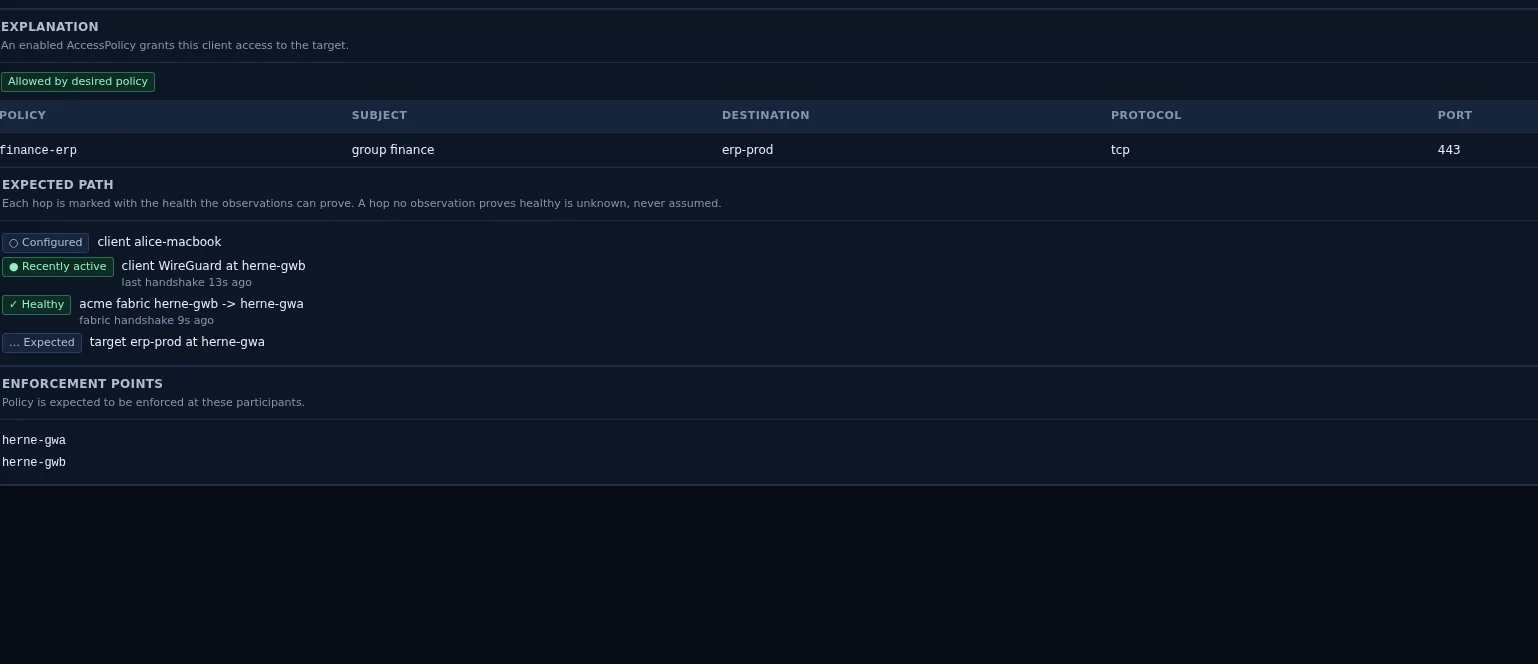
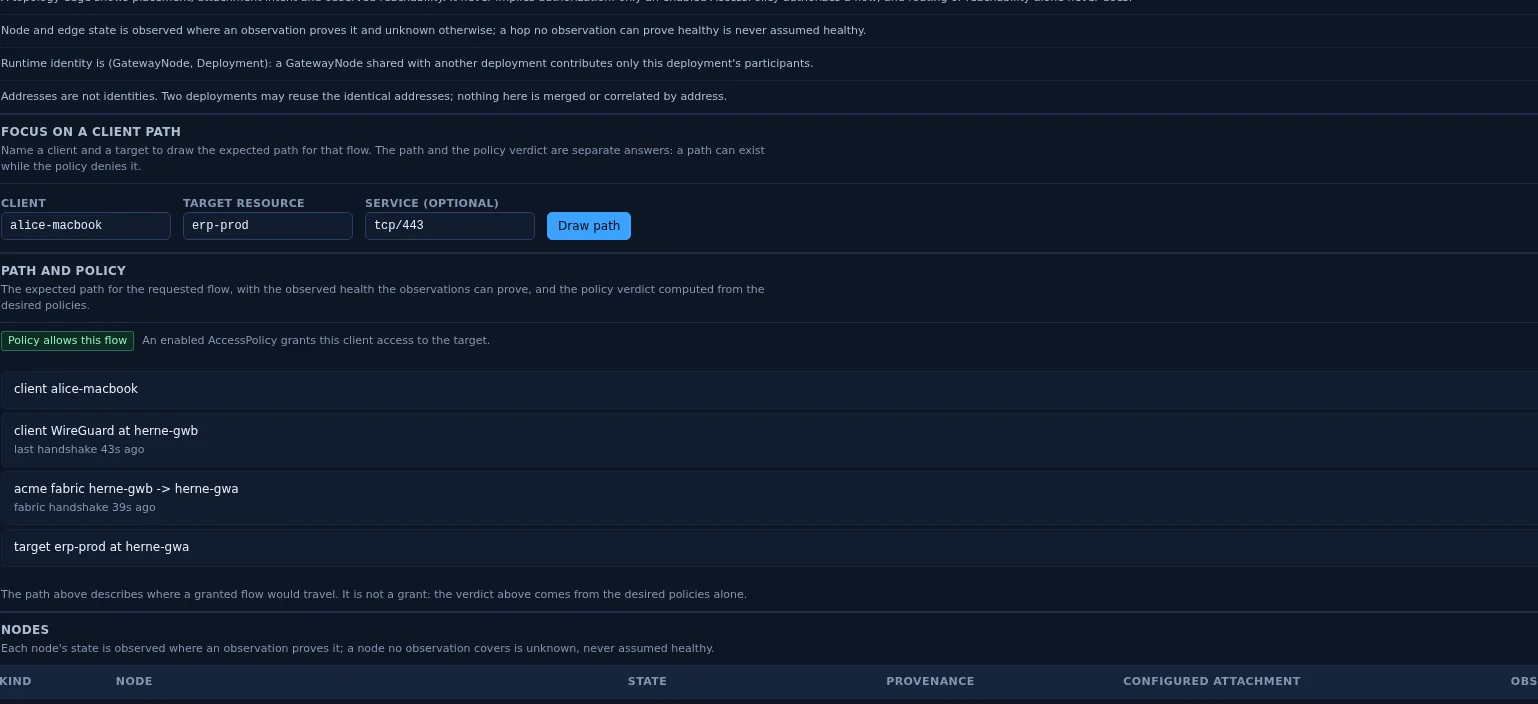
Not just “it works.” JANUS can explain why — or why not.
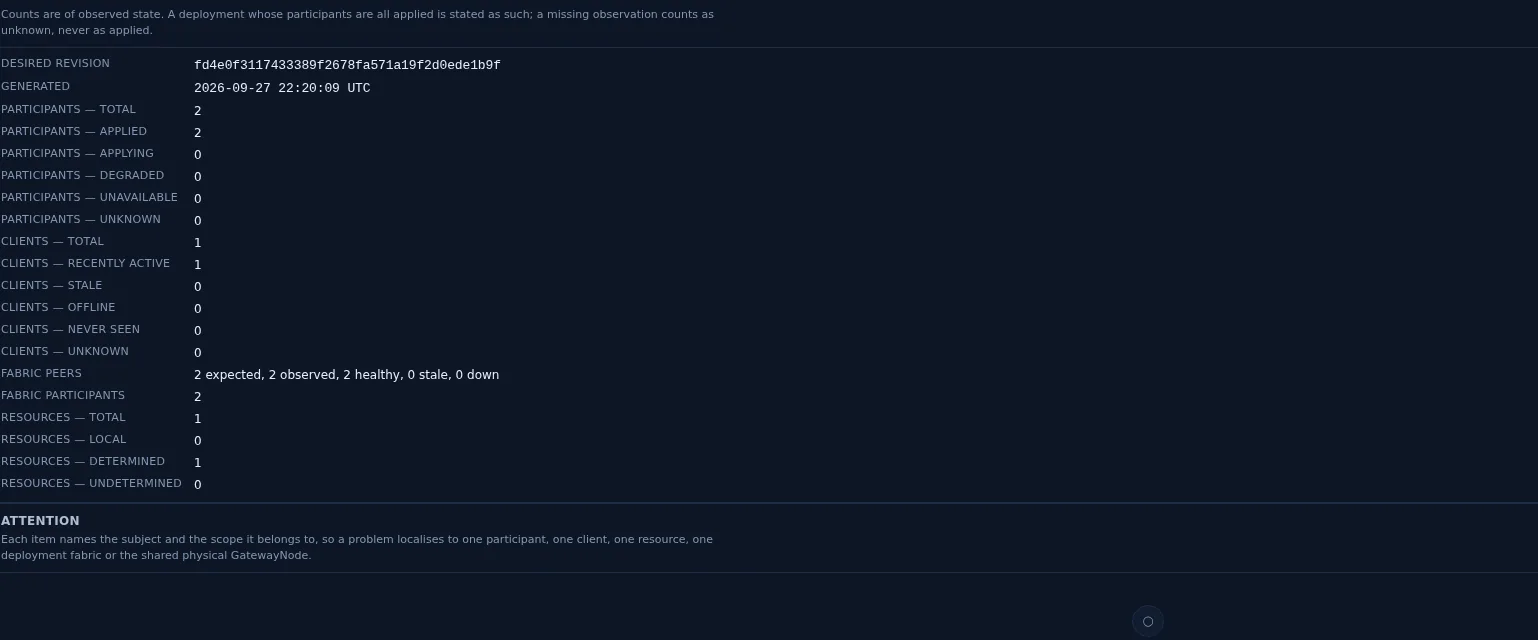
JANUS can make distributed runtime state visible and traceable, including gateway health, client activity, fabric state, resource reachability, desired versus applied state, and access-decision explanations.
Your infrastructure. Your choice.
JANUS is not a cloud-only service.
Operated for you
Korves.Net USA LLC operates dedicated JANUS infrastructure for the customer. Gateways can be placed in customer networks, data centers, branch offices and clouds.
Run it in your own infrastructure
JANUS can be operated entirely inside customer infrastructure — same product, same capabilities, no crippled edition.
Shared infrastructure, isolated runtimes
Shared physical infrastructure may host multiple customer deployments while each deployment runs in isolated network runtimes.
One product foundation. No technically crippled On-Prem edition.
No artificial bandwidth tiers.
JANUS should use what the underlying infrastructure can technically deliver. Commercial differentiation should not artificially throttle the packet path.
Current status
JANUS v1.0.0 is released and deployed in production — General Availability.
The platform includes distributed gateways and multi-ingress, policy-based access, runtime isolation per deployment, observability and reconciliation, MFA and passkeys, LDAP and Active Directory authentication, external identity providers, service identities and scoped administrative roles, among other capabilities.
We deliberately avoid unsupported claims about SLAs, scale limits or performance figures.
JANUS v1.0.0 — released, deployed in production, technically validated and documented.
Keep your routers. Keep your firewalls. Keep your infrastructure. Add JANUS — it complements existing infrastructure rather than replacing it.
See JANUS in motion
Let’s talk about JANUS.
We would be happy to show JANUS in a technical demonstration and discuss how it can fit into your environment.
- Korves.Net USA LLC
- 8 The Green, Dover, DE 19901, USA
- Email: service@korves.net
- Phone: +1 (201) 605-9444